Non-Human Identity Security: AI Agents as the IAM Blindspot
Traditional IAM perimeters fail against stochastic non-human workloads. Discover why AI agents represent a massive blindspot in your enterprise identity strategy.
Insights, guides, and updates on AI agent security, runtime protection, and enterprise compliance.

Traditional IAM perimeters fail against stochastic non-human workloads. Discover why AI agents represent a massive blindspot in your enterprise identity strategy.

Policy dashboards fail when applied to stochastic agents. Discover the structural blind spots inside your existing security stack (EDR, Firewall, IAM)

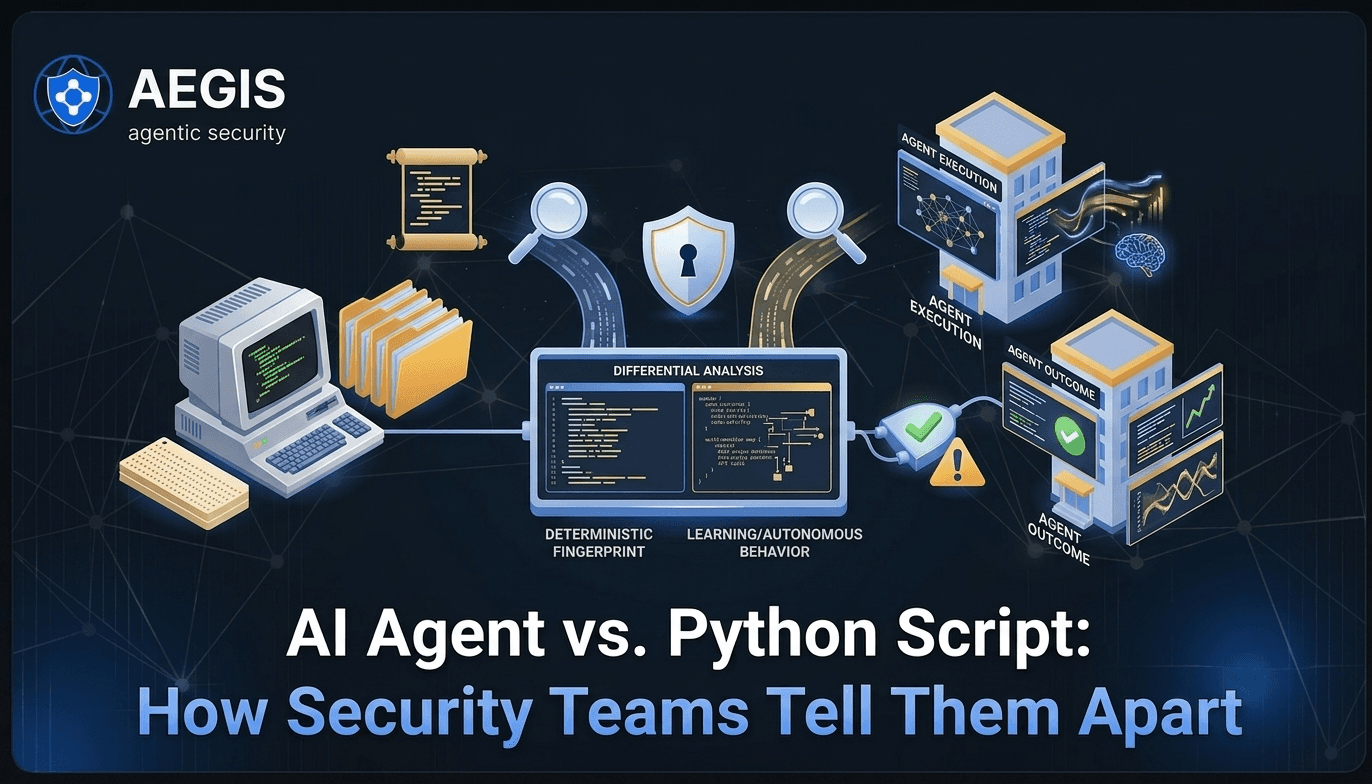
Policy dashboards fail when applied to stochastic agents. Discover the structural differences between linear scripts and autonomous non-human actors.

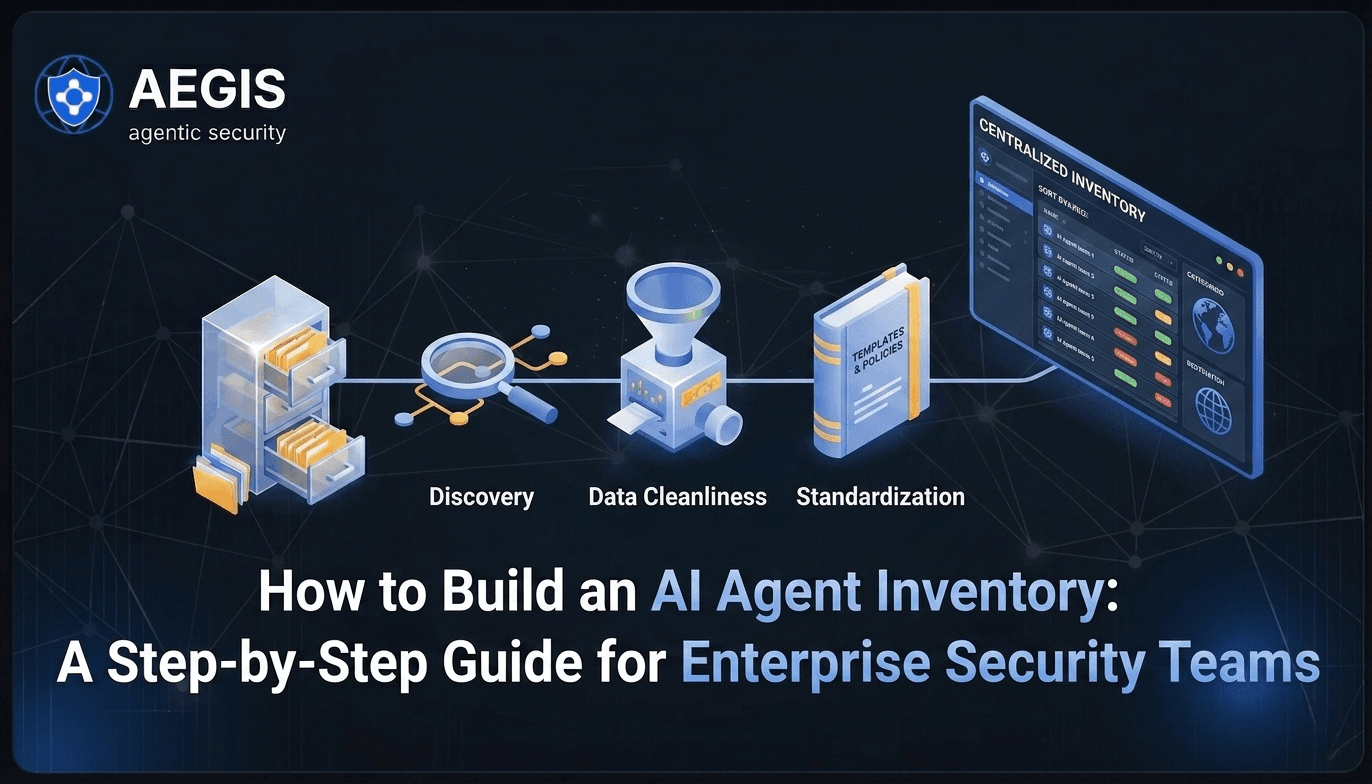
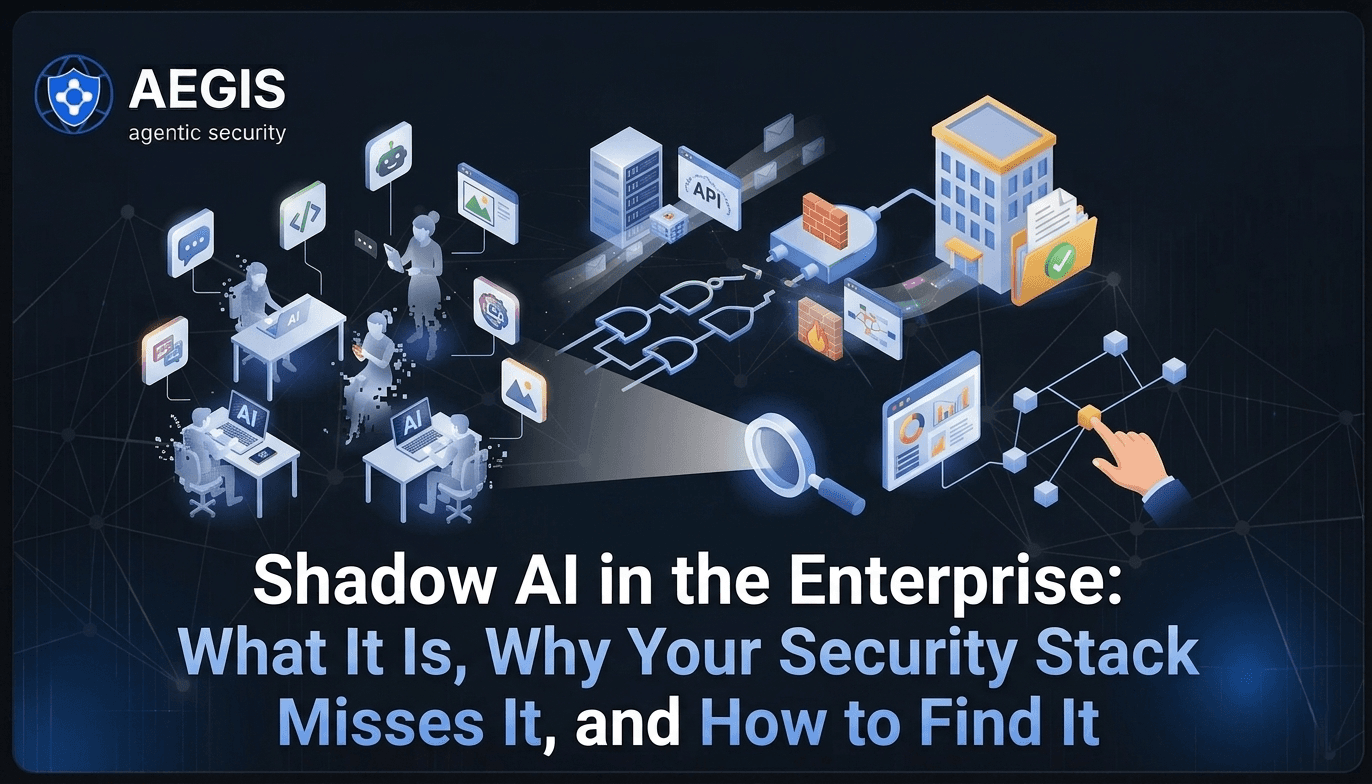
Step-by-step technical blueprint to construct a real-time AI agent inventory. Learn how to execute multi-plane correlation to find shadow AI agents.

Autonomous agents are multiplying faster than enterprise governance. Discover the technical drivers behind AI agent sprawl and how to implement runtime control blocks.

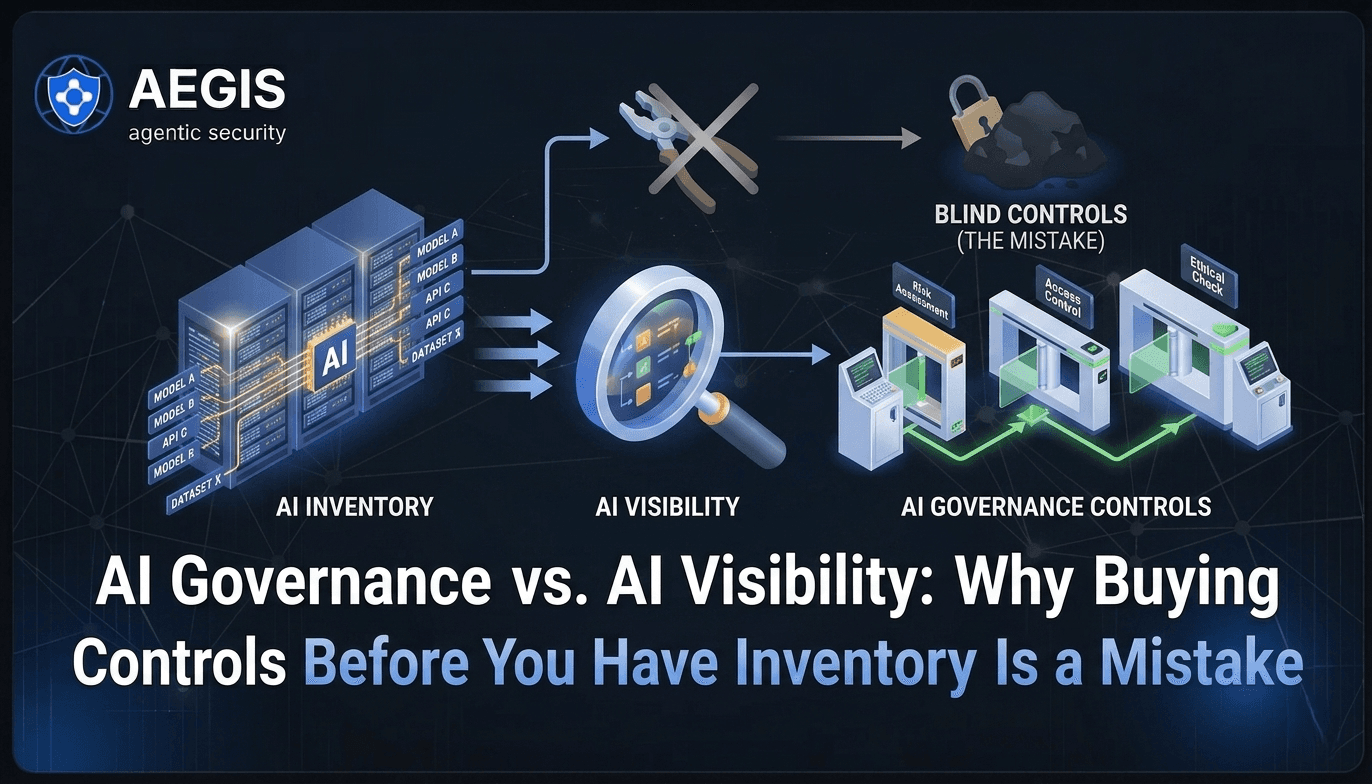
Policy dashboards assume you know what you are governing. Discover why enterprise AI governance fails without programmatic workload visibility and asset inventory.

Discover why traditional DLP and CASB engines fail to track conversational AI data leakage and how Aegis uses multi-signal correlation to eliminate the risk.

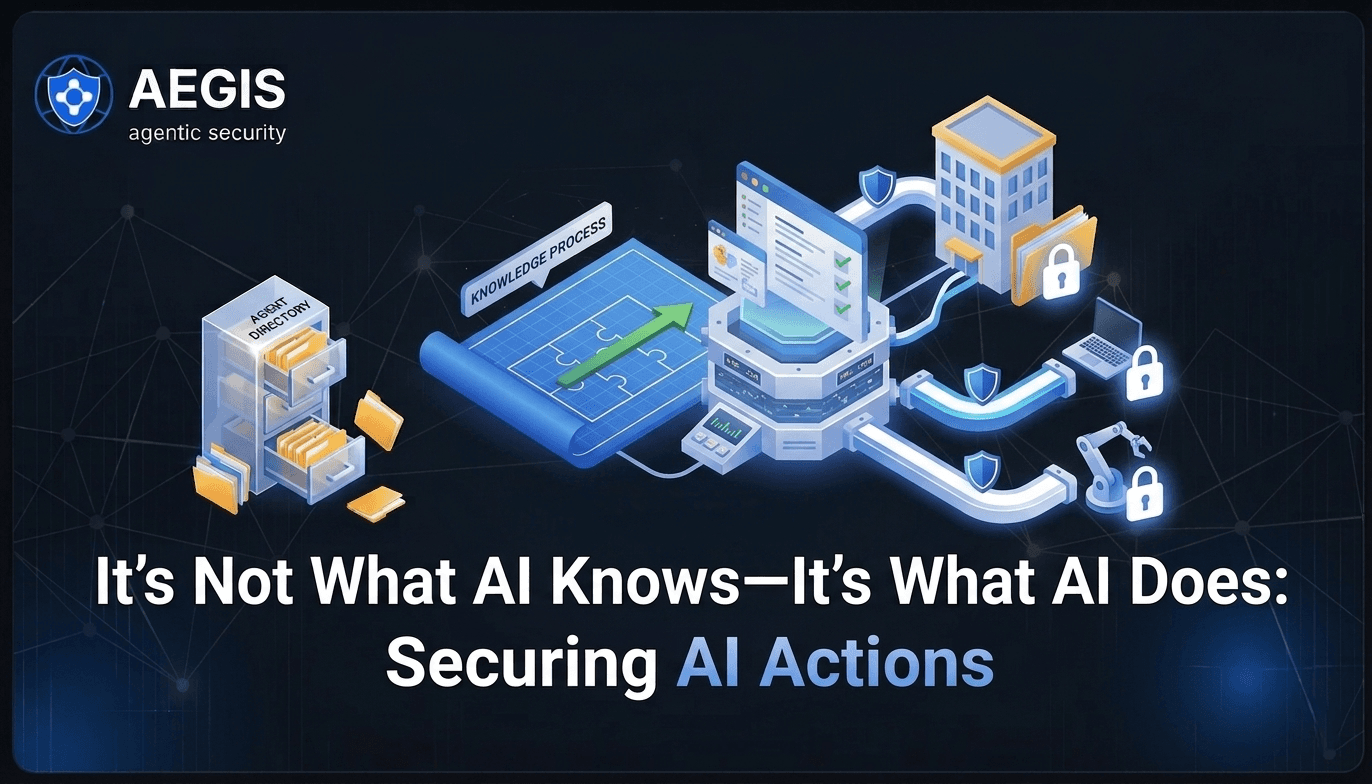
Shift your security focus from model outputs to runtime actions. Learn how to secure the AI execution layer using the Aegis runtime defense framework.

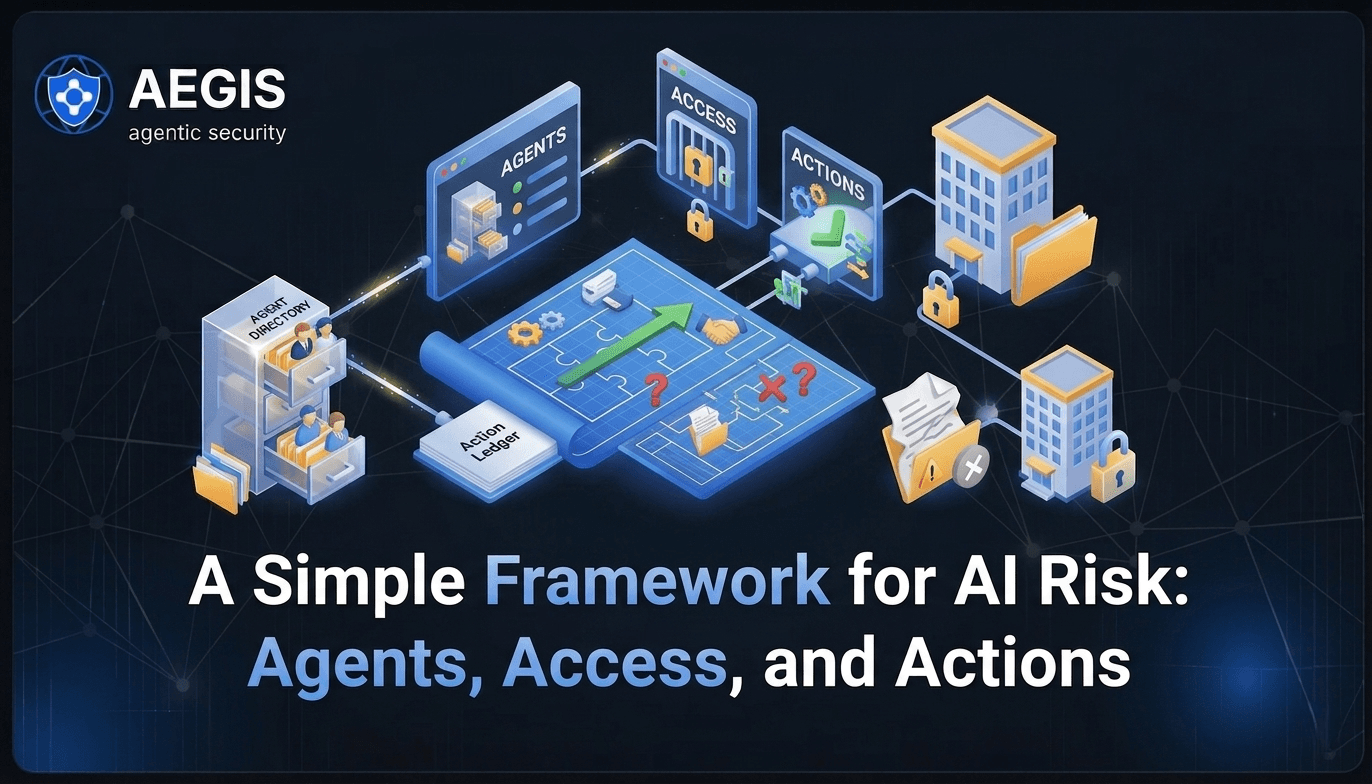
Move beyond static model posture. Learn how to implement the Agents, Access, and Actions (3As) runtime governance framework for autonomous AI systems.

Move beyond policy theater. Learn how to implement deterministic runtime enforcement, intent-based access, and an Agentic SOC to secure enterprise GenAI.

Explore the structural breakdown of traditional IT operations under the weight of autonomous AI sprawl and how to architect an AgenticOps control plane.

Explore the architectural risks of agentic AI. Learn how runtime enforcement and policy-as-code secure autonomous API and tool execution in the enterprise.