AI Agent Identity Security: Solving the Delegated Identity Problem
Master AI agent identity security by exploring the delegated identity problem, runtime authorization, OPA policy-as-code, and Envoy gateways for enterprise AI.
Practical guidance and perspectives on AI agent security, runtime protection, and enterprise compliance.

Master AI agent identity security by exploring the delegated identity problem, runtime authorization, OPA policy-as-code, and Envoy gateways for enterprise AI.

Discover why traditional service account IAM fails for AI agents. Explore runtime enforcement, Aegis architecture, and secure agentic governance.

Discover how AI agent identity is reshaping non-human identity (NHI) security. Learn how Aegis provides Zero Trust runtime enforcement, token exchange, and governance for autonomous agents.

Discover how to secure Model Context Protocol (MCP) servers in enterprise agentic workflows using Zero Trust runtime enforcement, identity-aware token exchange, and policy-as-code.

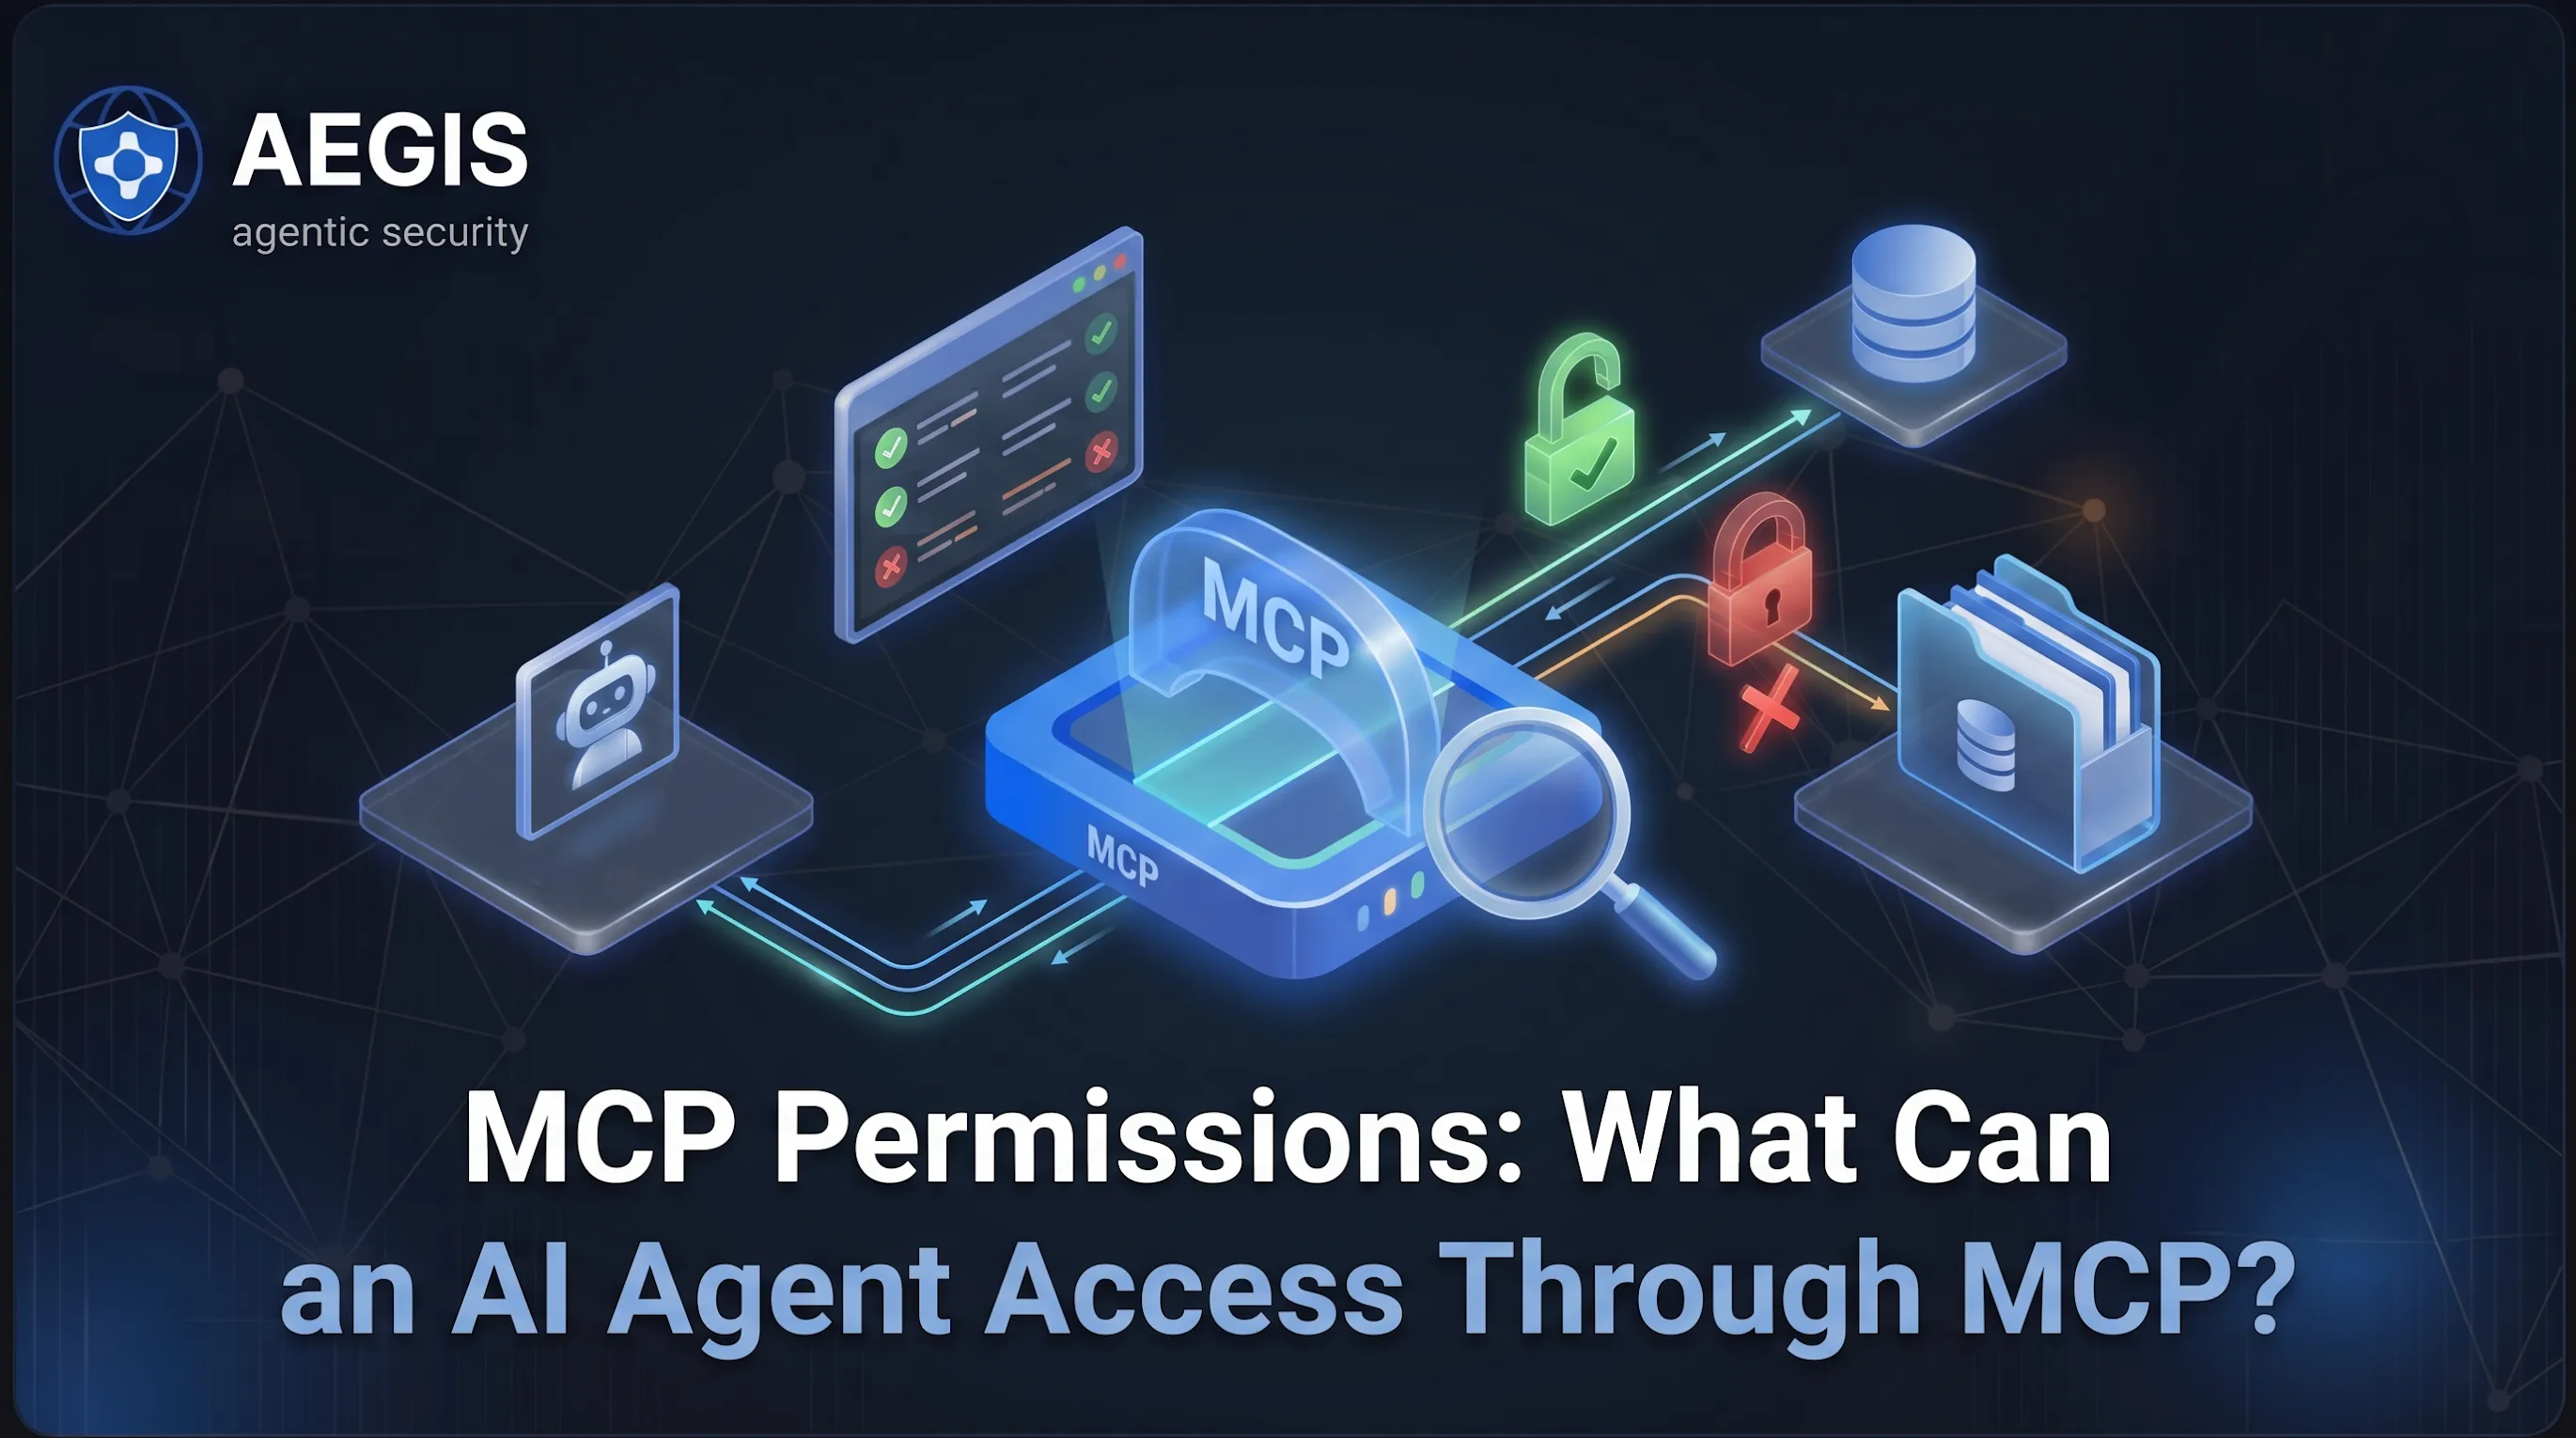
Master MCP permissions. Learn why coarse API tokens fail for AI agents and how to enforce fine-grained, runtime policy-as-code across Model Context Protocol.

Understand critical MCP security risks. Learn how Model Context Protocol alters enterprise attack surfaces and how runtime gateways block unauthorized tool execution.

Understand MCP server security risks. Learn why Model Context Protocol expands the enterprise attack surface and how runtime gateways block rogue tool execution.

Master MCP security. Learn how Model Context Protocol alters the enterprise attack surface and how to secure stdio and network transports with runtime proxies.

Understand how over-privileged AI agents create critical enterprise risk. Learn to eliminate standing privileges using runtime proxies and dynamic token exchange.

Move beyond authentication to runtime AI agent authorization. Prevent prompt injection, tool misuse, and data leakage using inline OPA policy enforcement.

Enforce AI agent least privilege. Learn why traditional IAM fails for non-human agents and how to secure dynamic tool execution with runtime proxy controls.

Evaluate AI agent permissions. Discover why static IAM roles fail, how to enforce dual-identity intersection, and how runtime gateways block unauthorized tool actions.